Offshore Data Processing under UK GDPR: Remote Access, IDTA and the Addendum
UK hosting does not settle the transfer question. If an overseas organisation can remotely access UK personal data, map the parties and apply the ICO's restricted-transfer test, then document any adequacy route, safeguard and data protection test that the facts require.
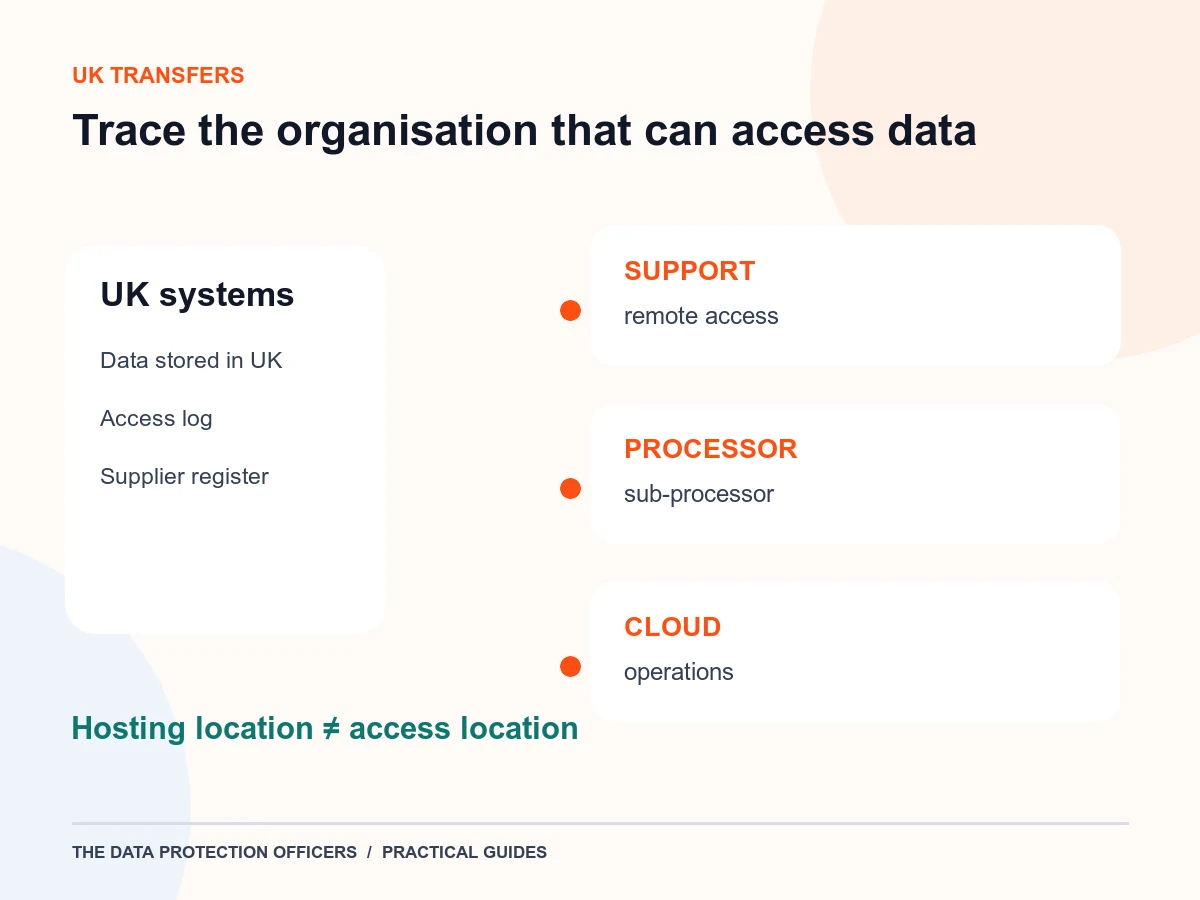
Start with the parties and access, not the server address
Identify the UK controller or processor, the receiving organisation, its location and who initiates the flow. Remote access from outside the UK can be a restricted transfer even if the server stays in the UK. Conversely, not every overseas technical event meets the same test. Apply the ICO's three-step restricted-transfer guidance to the actual arrangement.
Where a UK processor engages an overseas sub-processor, record the controller's authorisation, the processing agreement and the processor's transfer decision. Distinguish a separate receiving organisation from an employee travelling on behalf of the same organisation. Do not treat country of incorporation, hosting region and human access location as interchangeable.
Three illustrative data flows
These fictional examples are prompts for investigation, not conclusions that a particular transfer is lawful. The decision depends on the parties, destination, access rights and current adequacy position.
| Flow | Hosted / accessed | Question to resolve |
|---|---|---|
| UK company → overseas support supplier | UK cloud / support team outside UK | Is the supplier a separate receiver with remote access? Which safeguard and test apply? |
| UK processor → overseas sub-processor | UK or EU region / sub-processor outside UK | Has the controller authorised the sub-processor and who initiates the restricted transfer? |
| UK company → cloud provider | Selected region / provider operations may vary | Which legal entities and support locations can access personal data under the contract? |
Choose and document the transfer route
Check whether relevant UK adequacy regulations cover the destination and transfer. If not, consider an appropriate safeguard or a narrowly applicable exception. The ICO's International Data Transfer Agreement (IDTA) and the UK Addendum to EU Standard Contractual Clauses are contractual safeguard options; they are not generic names for a transfer assessment.
Before relying on a safeguard, complete the required transfer risk assessment, now called a data protection test in UK legislation. The ICO continues to use “TRA” in guidance. Assess whether protection after transfer would be materially lower and whether supplementary measures are needed. Revisit the analysis when destinations, access or law change.
Supplier information to request
Use a short fact sheet before drafting clauses. Ask for the contracting entity, all receiving entities, hosting regions, remote support locations, access roles, data categories, sub-processors, onward transfers, security controls and the available audit evidence. Record which statements come from the contract and which require technical confirmation.
A UK GDPR transfer route does not replace Article 28 processor terms, a lawful basis, transparency or security controls. Keep these workstreams connected but identify the separate decision for each.
| Field | Illustrative answer | Evidence to request |
|---|---|---|
| Hosting | UK region | Architecture and contract schedule |
| Remote access | Support in country X | Role list, logs and support policy |
| Onward parties | Ticketing sub-processor | Sub-processor list and change notice |
| Transfer route | To be assessed | Adequacy / IDTA or Addendum / data protection test |
Frequently asked questions
Does UK hosting avoid international transfer rules?
Not necessarily. An overseas organisation's remote access may be a restricted transfer. Apply the ICO test to the parties and actual access.
Does IDTA mean International Data Transfer Assessment?
In ICO guidance, IDTA means International Data Transfer Agreement. A transfer assessment or data protection test is a separate exercise.
Keep researching
Related resources
A practical next step
Make the next privacy decision clearer
Bring your organisation, processing, jurisdictions, current documents, internal owners, and deadline. We can help identify the right scope before an appointment or wider workstream begins.
This guide provides general information, not legal advice or a conclusion that a particular obligation applies. Confirm the legal scope and practical next steps against your organisation's facts.
Sources: ICO: International transfers, ICO: Are we making a restricted transfer?