US SaaS Launching in Europe: A GDPR Readiness Checklist
For an EU launch, map each processing activity and the US company's controller or processor role, then prepare notices, customer and vendor terms, transfer arrangements, rights and incident workflows, and separate decisions on DPIA, DPO and Article 27 representation.
Set the privacy scope before launch
This checklist covers GDPR and privacy readiness, not every legal requirement for selling software in Europe. Identify the legal entity, the people targeted in each market, any EU establishment and the activities that may bring processing into GDPR scope. A US company is not automatically a controller for every customer dataset; document its role for each activity.
Create a small data-flow inventory: account creation, billing, product telemetry, customer-hosted content, support, marketing and recruitment may have different purposes and roles. Record the EU country, affected people, data categories, recipients, retention and overseas access for each.
Build a launch evidence pack
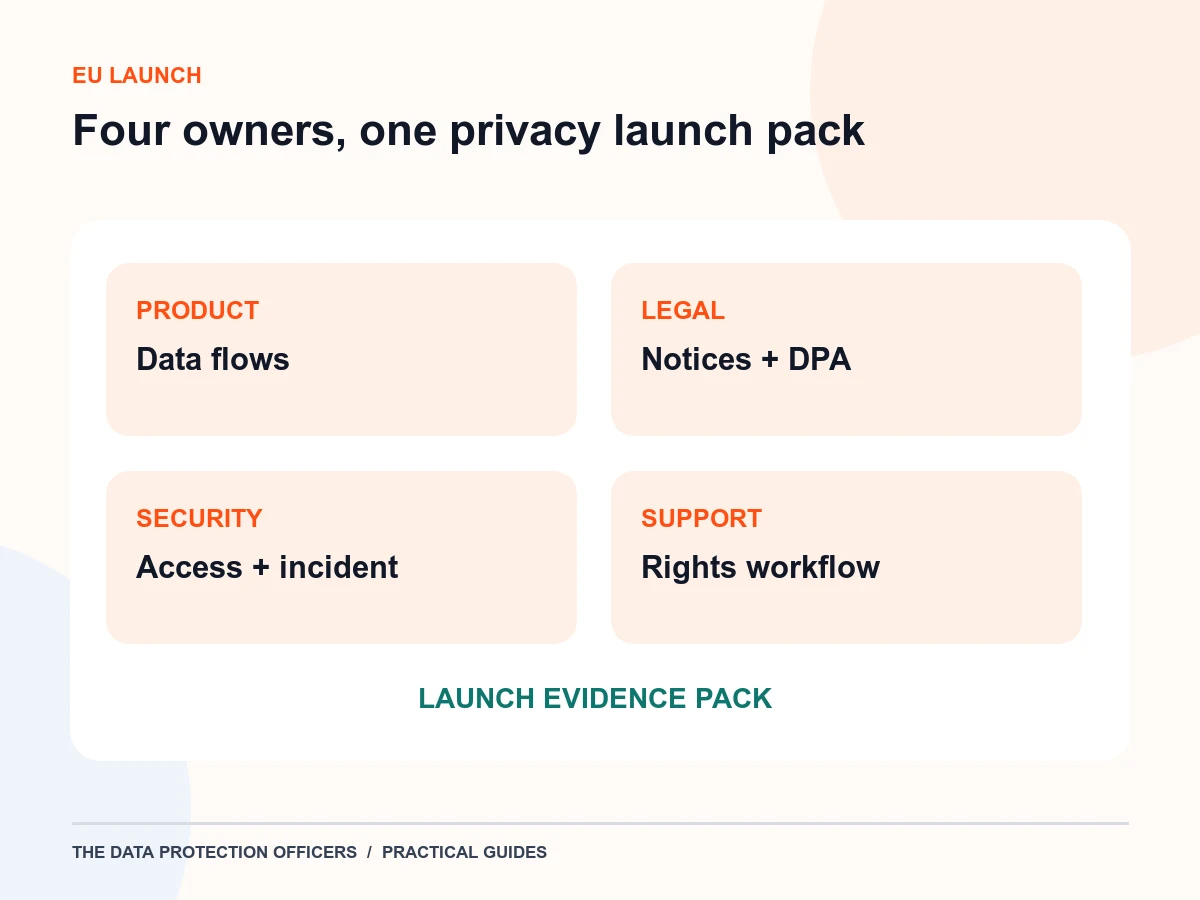
Use a shared tracker so each owner can show the actual approved document or tested workflow. A privacy notice that does not match the product or a DPA that omits a sub-processor is an open item, not a completed checkbox.
| Owner | Decision or deliverable | Evidence |
|---|---|---|
| Product | Data flows, retention and rights controls | Versioned diagram and test results |
| Legal / privacy | Controller/processor roles, notices, DPA, transfer route | Approved documents and decisions |
| Security | Supplier access, incident triage and safeguards | Access review and incident exercise |
| Support | DSAR intake and customer escalation | Routing test and response owner |
Make distinct role decisions
A GDPR Article 27 representative, a Data Protection Officer and a processor contact are different roles. Assess Article 27 territorial scope and exceptions separately from the Article 37 DPO criteria. An EU cloud region or local reseller does not itself establish either appointment. See the existing guides on EU territorial scope and the US SaaS representative appointment for the detailed role test.
Screen for a DPIA when planned processing is likely to present high risk to people. Record the reason for the decision even if no DPIA is required. Confirm an operational rights response and incident route before collecting EU user data.
Questions a customer may ask before signing
Prepare concise answers to: Which entity is the processor? Where can support staff access the data? Which sub-processors are used? How will you notify a customer of a security incident? Can you support access and deletion requests? Which transfer mechanism covers the relevant flow? Link each answer to a current contract, architecture record or procedure.
Recheck these answers after a new feature, provider or region changes the data flow. The launch pack is a starting operating record, not a one-time certificate of compliance.
Frequently asked questions
Does every US SaaS provider need an EU representative?
No. Assess the processing against GDPR territorial scope and Article 27 exceptions. The appointment question is distinct from DPO designation.
Is an EU cloud region enough for GDPR readiness?
No. Location is one fact; roles, lawful processing, transparency, contracts, rights, security and transfer access also need assessment.
Keep researching
Related resources
A practical next step
Make the next privacy decision clearer
Bring your organisation, processing, jurisdictions, current documents, internal owners, and deadline. We can help identify the right scope before an appointment or wider workstream begins.
This guide provides general information, not legal advice or a conclusion that a particular obligation applies. Confirm the legal scope and practical next steps against your organisation's facts.
Sources: EUR-Lex: GDPR, EDPB: Be compliant